A secure middleware layer is the better choice over direct system integrations when consistent security, centralized governance, and manageability are essential, especially in environments with strict compliance requirements and sensitive data flows.
Benefits of Middleware in Regulated Environments
In regulated environments, middleware offers significant advantages over direct API integrations. It centralizes security and governance, reduces operational risks, and increases the predictability of system behavior.
- Centralize security and governance to reduce inconsistencies and vulnerabilities.
- Manage operational risks with proactive monitoring and centralized error follow-up.
- Reduce maintenance effort through consistent rules for authentication and data transformation.
- Set up the processing of business-critical changes so that repeated requests remain manageable.
- Assess the impact of integration patterns on long-term predictability and manageability.
When middleware is preferable to direct integrations
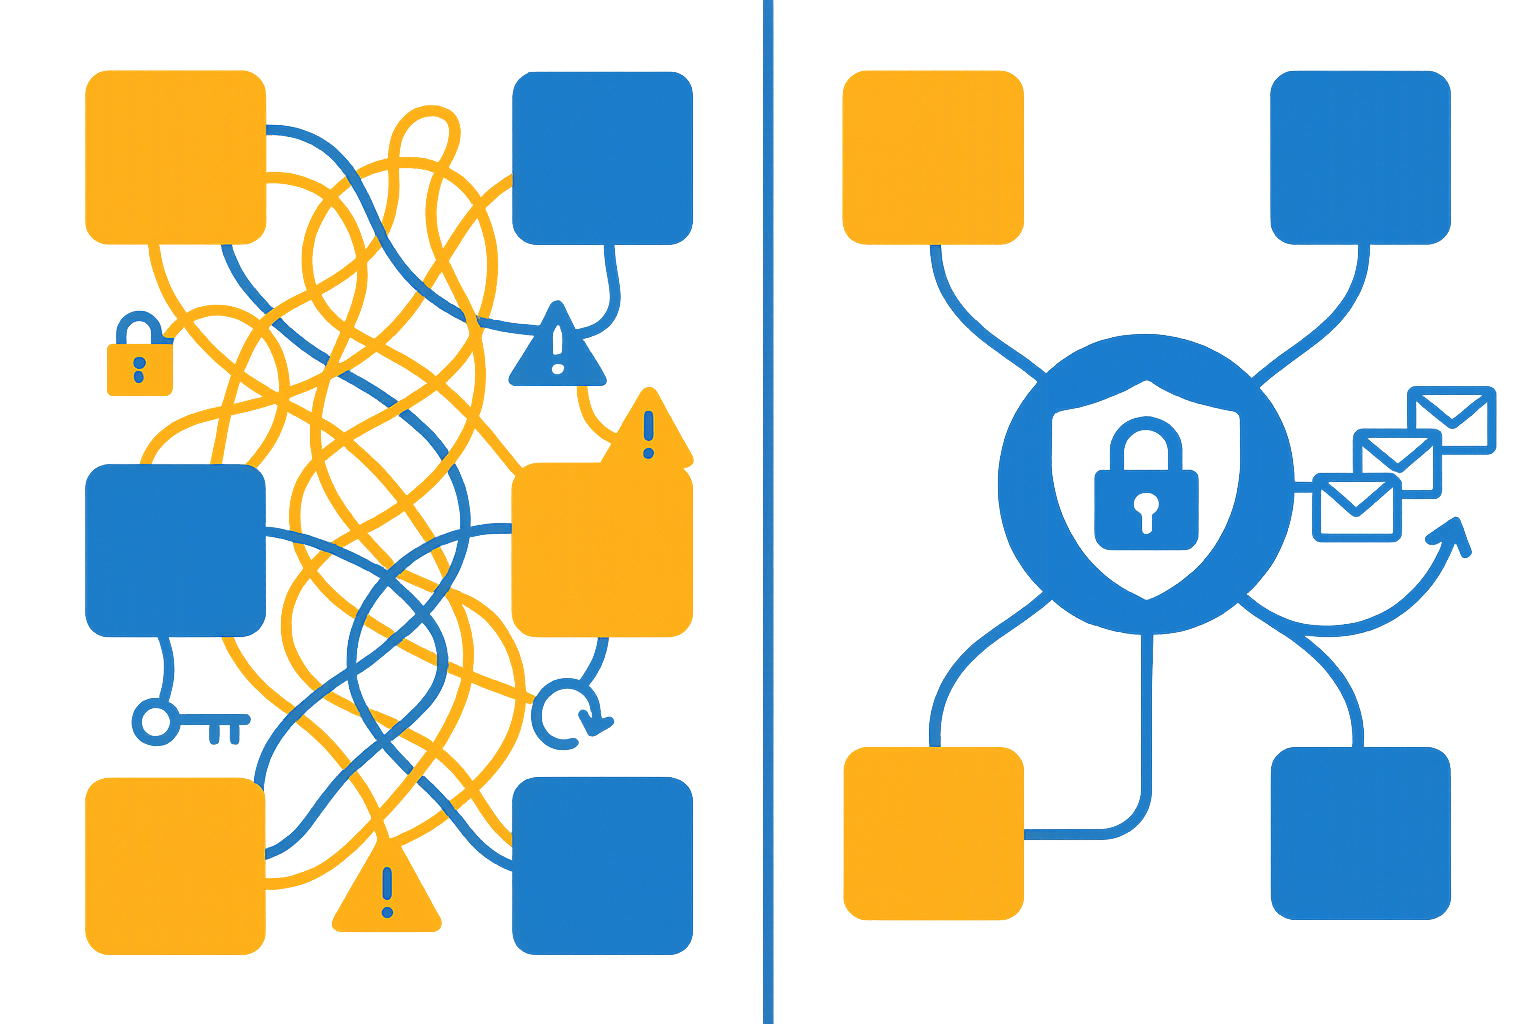
A middleware layer is preferable to direct integrations when consistent security, centralized governance, and manageability can no longer vary by application or team. In a landscape with multiple systems and sensitive data flows, direct point-to-point integration means that each source system becomes individually responsible for authentication, data transformation, rate limiting, and error handling. This results in fragmented implementations, where security measures and operational controls can differ per connection and maintenance increases as the number of connections grows.
By placing these recurring responsibilities in a middleware layer, the risk of inconsistencies and hidden vulnerabilities is reduced. Security rules, access control, and monitoring are no longer distributed across different applications, but are applied consistently and made transparent. This is particularly relevant in environments where compliance requirements, auditability, and traceability are central, and where deviations in security behavior are unacceptable.
Central orchestration also provides a fixed place for controlled processing of changes and exceptions. As a result, reliability does not depend on how each individual team handles retries, timeouts, and recovery. The specific implementation of this, including idempotency and queueing, deserves particular attention when administrative or financial changes are processed.
A middleware architecture also enables managed continuity: proactive queue monitoring, centralized telemetry, and SLA-backed error follow-up can become integral parts of the integration landscape. Whether this additional layer is appropriate therefore depends not only on the number of connections, but also on the consequences when a connection deviates, slows down, or fails.
Sources for this section: enterpriseintegrationpatterns.com, microsoft.com
Uncertainties When Choosing Integration Patterns
When choosing between direct integrations and a middleware architecture, uncertainty often arises about where the real management burden and risks will materialize. At first glance, point-to-point connections may seem straightforward and quick to implement, but in practice, work involving changes, error handling, and operational control becomes distributed across multiple applications and teams. This becomes apparent when, for example, an external supplier changes an API authentication standard: each internal application with a direct connection must then be modified separately, often under time pressure. If one team falls behind, a connection may fail unnoticed, leading to operational data discrepancies that must be corrected manually. Technical failures, such as a timeout during a transaction, can also create uncertainty about the processing status and therefore the recovery action required. These examples show that the choice of an integration pattern is not only about initial implementation speed, but above all about the long-term predictability of changes and incidents. The key question is therefore where responsibility for modifications, recovery, and oversight is best placed.
Sources for this section: microsoft.com
When Is a Comparison Between Middleware and Direct Integrations Relevant?
A comparison becomes relevant as soon as a connection does more than a single data exchange between two stable applications. Particularly when incoming data must first be validated consistently, token verification applies to multiple connections, or rate limiting must be enforced consistently, there is an architectural choice with implications for security and governance. A central middleware layer can perform these steps before domain logic is invoked. The assessment then shifts from whether an individual API is accessible to where consistent access and processing rules belong.
The urgency increases when connections are added as separate scripts under time pressure. This creates a web of dependencies in which a schema change in one place can trigger unpredictable chain reactions. In that situation, a direct connection is no longer merely a local technical choice: every new connection affects the manageability of the whole. The comparison between both patterns should therefore be considered as soon as the application landscape grows, security rules are repeated, or changes in one interface can affect multiple systems.
In this context, middleware is not an end in itself. The layer is relevant because it provides a place for consistent validation, token verification, and traffic limiting. Direct integrations remain suitable when these responsibilities genuinely remain limited and local; once they spread across multiple connections, coherence becomes more important than the speed of one individual connection.
Sources for this section: microsoft.com, microsoft.com, ncsc.nl
Comparison Factors for Middleware and Direct Integrations
The comparison below focuses on factors that determine where security and governance are placed within the integration landscape. The difference is not solely in the route data takes, but in the extent to which processing and security behavior can remain consistent as systems and teams change alongside each other.
| Factor | Direct integration | Middleware layer | Implication for governance |
|---|---|---|---|
| Data format and distribution | The translation of data is defined per connection. When multiple recipients each expect a different data format, that translation logic emerges in different places. | Data orchestration can normalize incoming information flows into a single canonical data model. Transformed messages can then be distributed asynchronously to connected systems through controlled queue workers. | The organization can manage the definition of the data format centrally, rather than allowing the same meaning to be recreated for each connection. |
| Security behavior | Application teams each build authentication and rate limiting separately. As a result, security behavior may differ between connections. | A central layer provides one place to apply recurring rules in the integration flow. | The question shifts from the quality of one implementation to control over one shared security policy. |
| Differences between teams | Separate implementations can result in outdated TLS versions or API tokens that are not logged. This makes the level of security dependent on local choices and maintenance. | Centralization reduces the need to maintain the same security logic again in every application. | Governance gains a concrete point of control for assessing deviations, rather than a collection of different controls per application. |
Sources for this section: enterpriseintegrationpatterns.com, owasp.org, microsoft.com, ncsc.nl
Trade-offs When Choosing Middleware or Direct Integrations
The decision is not about adding a layer for architecture's sake, but about what error behavior operations can accommodate. The points below show what an asynchronous, centrally managed processing path adds compared with a model without controlled queueing and centralized idempotency.
- Isolation of temporary failures versus direct dependency. Asynchronous queue processing with automatic retry policies, exponential backoff, randomized jitter, and persistent dead-letter queuing can isolate temporary API failures. This means a temporary failure does not have to cascade into failures in source systems. The trade-off is that processing is not approached solely as a direct-response pattern: messages are processed in a controlled way and exceptions remain available for follow-up through the dead-letter queue. This makes the error flow an explicit part of the integration architecture.
- Controlled processing versus data inconsistency. For administrative changes, centralized idempotency can prevent a repeated request after a timeout from being performed again. With, for example, unique Idempotency Keys, the same change can be recognized, making duplicate order processing, incorrect inventory levels, and manual reconciliations less likely. The trade-off is therefore not only development effort, but also the choice between explicitly managed error behavior and the cost of corrections afterward.
However, middleware is not automatically the better choice. For a single, low-volume connection between stable systems, a direct integration can be clearer and require fewer operational components. An additional layer brings its own costs, management needs, potential latency, and availability requirements. Its added value arises primarily when reusable controls, multiple recipients, or controlled recovery outweigh that additional complexity.
Sources for this section: enterpriseintegrationpatterns.com
Frequently Asked Questions About Middleware and Direct Integrations
Frequently asked questions about middleware and direct integrations often focus on the balance between speed, operational complexity, and the way risks are managed. Two recurring questions are answered below from the perspective of security and governance:
- “Isn't a direct connection quicker to implement?” For a single, well-defined integration, a point-to-point connection can indeed become operational more quickly. This advantage applies particularly as long as the application landscape remains limited. Once the number of systems or variation in security and compliance requirements increases, the operational burden grows: each new connection requires its own coordination, monitoring, and modification when changes occur. The initial speed advantage can then turn into a structural management effort, because modifications and controls must be implemented across multiple systems.
- “Doesn't middleware itself become an additional single point of failure?” A central middleware layer requires high availability and robust monitoring because it forms a visible hub in the architecture. This creates a clear dependency. At the same time, centralization prevents vulnerabilities and inconsistencies from spreading unnoticed across separate applications. Rather than many separate risks in different places, management becomes concentrated and more transparent. The choice therefore comes down to where you want to manage risk: distributed across multiple connections with limited visibility, or centrally with explicit requirements for availability and control.
Sources for this section: microsoft.com, microsoft.com
Key Considerations When Choosing Middleware or Direct Integrations
Selecting an integration partner requires verifiable signals about how that party handles recurring integration problems and security. What is decisive is not the presence of an additional layer, but demonstrable evidence that patterns, error scenarios, and security measures have been deliberately designed, documented, and can be assessed. For an organization seeking to limit the cost of disruptions or manual corrections, the following criteria provide a concrete basis for evaluation.
- Ask for demonstrable use of formal integration patterns. Relevant signals include experience with a Message Router, Content Enricher, Idempotent Receiver, and Dead Letter Channel. These patterns show how messages are routed, enriched, protected against duplicate processing, and handled when regular processing fails. The value of this question is not in checking off names, but in the ability to assess concrete choices against the organization's integration flows. A partner that can substantiate these patterns can explain where exceptions end up and how processing behaves when a normal path is unavailable.
- Ask for documented API security measures. A substantiated approach includes documentation of measures against the OWASP API Security Top 10 and aligns with the NCSC security guidelines for web applications and APIs. In contexts where GDPR or NIS2 obligations are relevant, such documentation helps make security choices, access control, and error handling more assessable. Documentation thereby makes security assessment part of the selection process rather than an assumption after delivery. Unclear measures leave uncertainty about the protection of interfaces and increase the risk of recovery work in operations when failures occur.
Sources for this section: enterpriseintegrationpatterns.com, owasp.org, ncsc.nl